
Esiste un collegamento diretto con Belgrado, in Serbia, e ci sono, o c'erano, numerosi dipendenti Dominion in Serbia. Sempre in Serbia esiste la Open Society Foundation, proprieta' di Soros, che appartiene ad una delle 1/2
➡️Found IP address in the Dominion Server,kidnapped in Frankfurt,2020 US elections manipulating actors:
👉Belgrade,Serbia(OSF/Soros)
👉Iran(Edison/BMA)
👉HSBC Bank,Canada(Eric Coomer)
👉DVSCORP(UNICOM China)
👉CTCL(Mark Zuckemberg)
👉Indivisible .org(ACORN,OBAMA Political Group)
Esiste un collegamento diretto con Belgrado, in Serbia, e ci sono, o c'erano, numerosi dipendenti Dominion in Serbia. Sempre in Serbia esiste la Open Society Foundation, proprieta' di Soros, che appartiene ad una delle 1/2

I clienti di Edison Research includono Activision,Amazon,AMC Theatres, Apple,Disney,Dolby Laboratories, Facebook,Google,Oracle,The US 2/4
società avesse notato queste o altre anomalie nei dati di voto, il presidente di Edison Research 👉Larry Rosin ha 3/4
https://t.co/Iz3tjq37ZR


More from Internet


SolarWinds follow up. Very good tweet explaining what happened.
Basically what this means is that SolarWinds itself was exploited. Someone posted an infected update as legitimate (digitally signed), leading customers to download a bad update.
“Multiple trojanized updates were digitally signed from March - May 2020 and posted to the SolarWinds updates website” https://t.co/8e3bMFWXYu

FireEye then explains that infected organizations were approached and exploited. This is a separate Step 2.
At this point, information is already going to “malicious domains” without extra intervention, after the malware does nothing for “up to two weeks”

Hackers reportedly slipped malware into prior SolarWinds software updates, which gave them access to a "God-mode" for infected networks, including the Treasury and Commerce departments.
— Wes Wilson (@weswilson4) December 14, 2020
The Pentagon is also a SolarWinds customer.https://t.co/Srcoztssol https://t.co/OgMhAjJqPx
Basically what this means is that SolarWinds itself was exploited. Someone posted an infected update as legitimate (digitally signed), leading customers to download a bad update.
“Multiple trojanized updates were digitally signed from March - May 2020 and posted to the SolarWinds updates website” https://t.co/8e3bMFWXYu
FireEye then explains that infected organizations were approached and exploited. This is a separate Step 2.
At this point, information is already going to “malicious domains” without extra intervention, after the malware does nothing for “up to two weeks”


Well, this should be a depressing read -- notably because the UK and the US are both terrible when it comes to data protection, but the UK appears to be getting a pass. So much for 'adequacy'.
A few initial thoughts on the Draft Decision on UK Adequacy: https://t.co/ncAqc93UFm
The decision goes into great detail about the state of the UK surveillance system, and notably, "bulk acquisition" of data, and I think I get their argument. /1
For one, while the UK allows similar "bulk powers," it differs from the US regime both in terms of proportionality, oversight, and even notice. Some of this came about after the Privacy International case in 2019 (Privacy International) v Investigatory
Powers Tribunal [2019]) /2
Whereas, other bits were already baked in by virtue of the fact that the Human Rights Act is a thing (This concept doesn't exist in the US; rather we hand-wave about the Constitution and Bill of Rights, and then selectively apply it) /3
For example, UK bulk surveillance (I'm keeping this broad, but the draft policy breaksk it down), substantially limits collection to three agencies: MI5, MI6, and GHCQ). By contrast, it's a bit of a free-for-all in the US, where varying policies /4
At least we have a draft of the adequacy decision. I haven't read it yet, mostly because I'm afraid I'll be disappointed that it doesn't address the UK's penchant for surveillance. https://t.co/puJiVET2SJ
— Don Edwards (@DMEdwards) February 20, 2021
A few initial thoughts on the Draft Decision on UK Adequacy: https://t.co/ncAqc93UFm
The decision goes into great detail about the state of the UK surveillance system, and notably, "bulk acquisition" of data, and I think I get their argument. /1
For one, while the UK allows similar "bulk powers," it differs from the US regime both in terms of proportionality, oversight, and even notice. Some of this came about after the Privacy International case in 2019 (Privacy International) v Investigatory
Powers Tribunal [2019]) /2
Whereas, other bits were already baked in by virtue of the fact that the Human Rights Act is a thing (This concept doesn't exist in the US; rather we hand-wave about the Constitution and Bill of Rights, and then selectively apply it) /3
For example, UK bulk surveillance (I'm keeping this broad, but the draft policy breaksk it down), substantially limits collection to three agencies: MI5, MI6, and GHCQ). By contrast, it's a bit of a free-for-all in the US, where varying policies /4


You May Also Like







First update to https://t.co/lDdqjtKTZL since the challenge ended – Medium links!! Go add your Medium profile now 👀📝 (thanks @diannamallen for the suggestion 😁)
Just added Telegram links to https://t.co/lDdqjtKTZL too! Now you can provide a nice easy way for people to message you :)
Less than 1 hour since I started adding stuff to https://t.co/lDdqjtKTZL again, and profile pages are now responsive!!! 🥳 Check it out -> https://t.co/fVkEL4fu0L
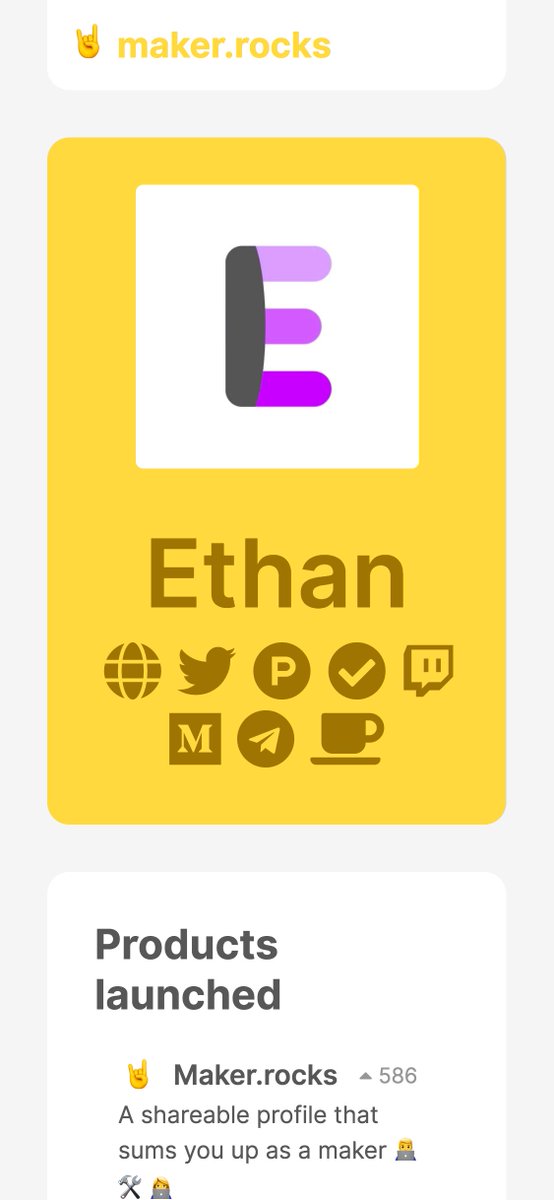
Accounts page is now also responsive!! 📱✨
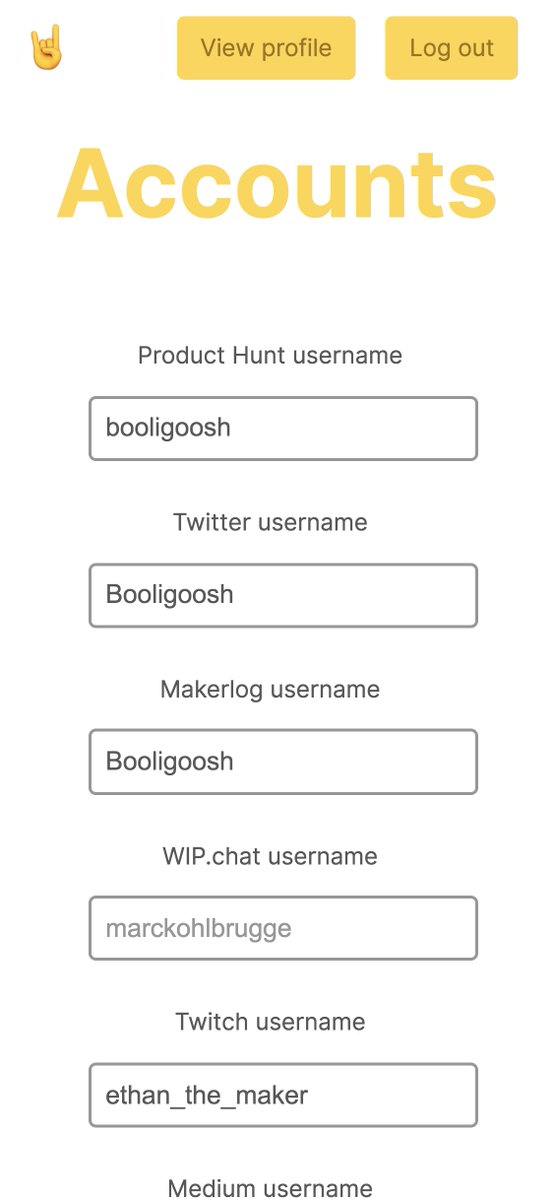
💪 I managed to make the whole site responsive in about an hour. On my roadmap I had it down as 4-5 hours!!! 🤘🤠🤘
Just added Telegram links to https://t.co/lDdqjtKTZL too! Now you can provide a nice easy way for people to message you :)
Less than 1 hour since I started adding stuff to https://t.co/lDdqjtKTZL again, and profile pages are now responsive!!! 🥳 Check it out -> https://t.co/fVkEL4fu0L
Accounts page is now also responsive!! 📱✨
💪 I managed to make the whole site responsive in about an hour. On my roadmap I had it down as 4-5 hours!!! 🤘🤠🤘