Wanna disable Defender when enabled Isolated Core and Tamper protection?

Its a bit more trouble- but doable, without ruining Isolated Core/Secureboot etc.

Defenders process will run as a unkillable protected service- so new tricks needed.

Here we go:

Ok- tamper protection is easy, just make .bat - run as adm:
:again
reg add "HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\WdFilter\Instances\WdFilter Instance" /v altitude /t REG_SZ /d -1 /f
goto again

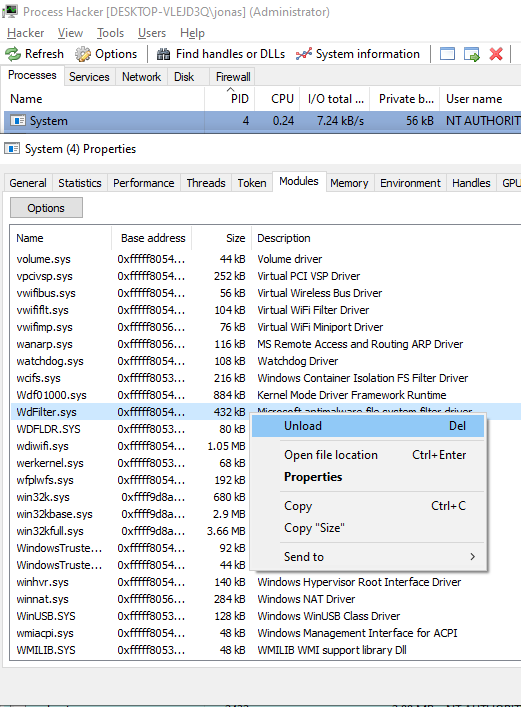
Then unload minifilter with process hacker:
The registry key will be changed while the minifilter do not protect it, when tamper protection makes the driver load again it cannot attach to volumes nor protect registry keys.

Removing it will make it recreate, but invalid altitude do the trick
Notice now the service is: Protected light(antimalware)
Now we cant do anything to the service/process- not even see its open handles.
Lets start by elevating to SYSTEM- just launch a command prompt, then close process hacker- and run it again from the command prompt.
Now process hacker runs as SYSTEM
Find the services process again- select the token tab.

Right click and disable the two groups:

WinDefend
Administrators
https://t.co/vSDPatKkXK
Now defender no more constant opens files- it dosnt do anything actually....

If you wanna permanently disable it its easy enough now there is no protection on its files.

If you mklink MsMpLics.dll:q nul it will not run on restart- but you loose the isolated core status :S
But secure boot and core isolation is still running fine
I am surprised that the protected services tokens are not protected.... that seems like bad design...

It also means we can impersonate them- here I impersonate SecureSystem:

More from Internet

Many conversations happening on #WhatsApp (WA) groups about new #WhatsAppPrivacyPolicy .
This thread has arguments to help ditch WA & move to @signalapp:
https://t.co/En4fe9VxUN
Share, use, copy-paste, modify with understanding as you deem fit on any platform in whole or part
1/n

Note: No affiliations, conflict of interest
Info presented with NO bias, prejudice, malice or indemnity.
Open to corrections: individual tweets may be deleted, tweets added to thread or corrected as replies.
Points that are unclear or uncertain are marked with "(?)".
2/n

CONTENT OF WA MESSAGES SHALL REMAIN ENCRYPTED END TO END.
BUT, there's data: contacts, group affiliations, co-affiliations, locations (live?), frequency of contacts, *tags* generated when we send or forward a message or file to contacts or groups, links, clicks on links, etc.
3/n

It is unclear whether this data is anonymized.
NOTHING in latest policy *prevents* the collection, retention, sharing or sale by FaceBook (FB: owner of WA) of this data in part or whole whether with identifying information or anonymized.
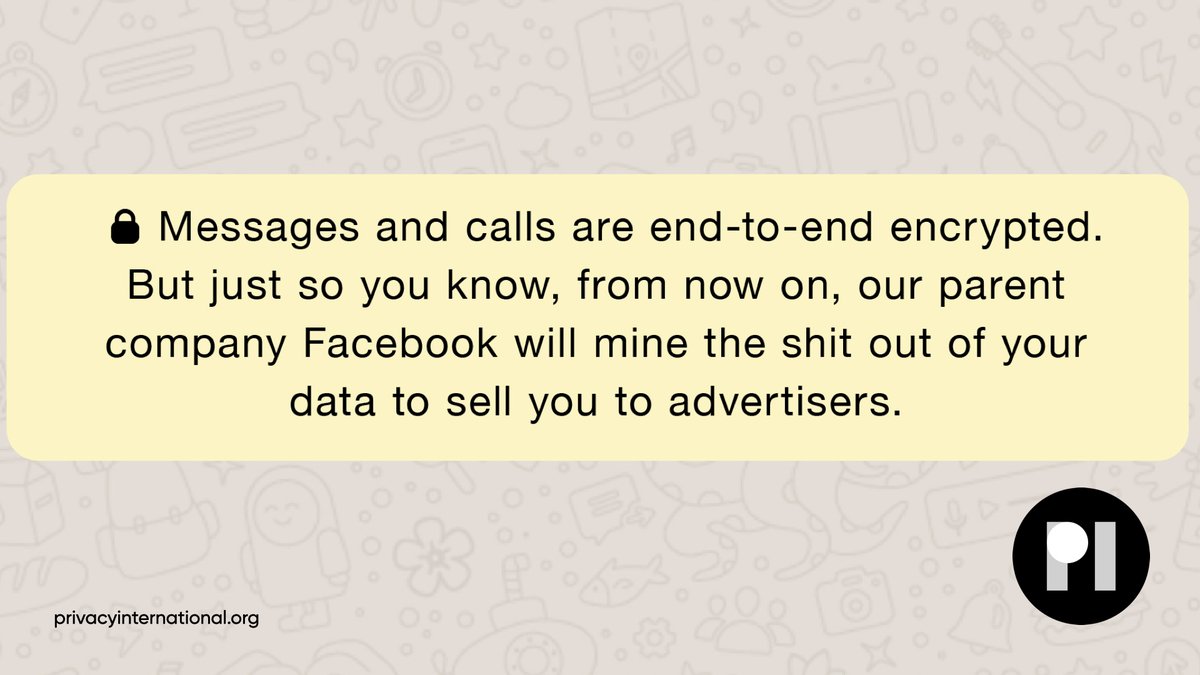
Meme source:
https://t.co/nMDTUlb0rl
4/n


Companies need to make money & generate profits:
To create software, install & maintain infrastructure.
Google, FB, Insta, Amazon etc sell data created from our content & data generated from our interactions (searches, clicks, purchases etc).
This makes many uncomfortable.
5/n

You May Also Like